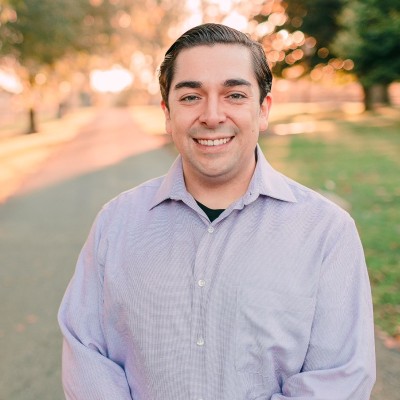
Michael Long
Senior Security Engineer at Amazon Web Services (AWS)
Columbia, Maryland, United States


Summary
🤩
Rockstar🎓
Top SchoolMichael Long is a Senior Security Engineer at AWS with eight years of cybersecurity experience and a background as a U.S. Army Cyber Operations Specialist. He previously shaped adversary emulation at MITRE and now focuses on cloud-scale security research and engineering in Columbia, Maryland. A hands-on practitioner, he contributes to Metasploit by developing post-exploitation modules that improve persistence techniques and tooling for Linux and Windows, reflecting deep offensive tradecraft. Academically anchored with an MS from SANS and PhD studies in Cyber Operations, he bridges rigorous research with practical red-team capabilities. Known for translating adversary behaviors into defensible controls, he brings military discipline and open-source impact to cloud security challenges.
 8 years of coding experience
 4 years of employment as a software developer
 Bachelor’s Degree, Information Technology, Bachelor’s Degree, Information Technology at American Military UniversityMaster of Science (M.S.), Information Security Engineering, Master of Science (M.S.), Information Security Engineering at SANS Technology InstituteStudent - PhD in Cyber Operations, Student - PhD in Cyber Operations at Dakota State University

Github Skills (12)
security10
powershell10
exp10
point-of-sale10
penetration-testing10
pos10
metasploit10
python9
ruby9
bash8
linux8
windows8
Programming languages (8)
Github contributions (5)
rapid7/metasploit-framework
Dec 2019 - Mar 2020
Metasploit Framework
Role in this project: Security Engineer
Contributions:6 commits, 4 PRs, 18 comments in 3 months
Contributions summary:Michael primarily contributed to the Metasploit Framework by developing and integrating modules for post-exploitation activities. These modules focused on establishing persistence on target systems, particularly through modifying the Bash profile on Linux systems and installing OpenSSH server and client for Windows, and installing Python. The user also refactored code to incorporate the Msf::Post::Windows::Powershell mixin and added support for specifying Python versions, indicating a focus on improving the framework's capabilities for penetration testing and post-exploitation tasks.
metasploit
bluesentinelsec/OffensiveGoLang
Oct 2019 - Mar 2022
A collection of Offensive Go packages.
Contributions:1 release, 16 commits, 6 PRs in 2 years 5 months
go-packages
Find and Hire Top DevelopersWe’ve analyzed the programming source code of over 60 million software developers on GitHub and scored them by 50,000 skills. Sign-up on Prog,AI to search for software developers.